WEB APPLICATION SECURITY TRAINING FOR DEVELOPERS
- Services
- AI-centred Security
- Trainings & Workshops
- Web Application Security Training for Developers
Learn to think like an attacker
Critical security vulnerabilities are increasingly being found in newly developed software. To avoid financial loss and damage to reputation, effective security must be embedded right from the development phase, in line with the ‘shift-left’ principle.
In our one-day practical workshop, designed specifically for developers, we show dev teams how to reliably identify vulnerabilities in their web applications by adopting the attacker’s perspective. After all, only those who can attack their system can defend it.
Are you interested in our workshop? Please feel free to get in touch with us:
Course content – What you will learn
In a compact one-day workshop, two experienced security experts will equip you and your team to identify vulnerabilities in an application and respond to them in line with OWASP best practices.
- You will learn about the Top 10 vulnerabilities as defined by OWASP.
- You will gain practical experience in using a common security tool for vulnerability analysis.
- You will learn to view an application from an attacker’s perspective and uncover vulnerabilities.
- You will be able to identify and rectify the most common vulnerabilities in web applications, ranging from weak authentication, through injections and cross-site scripting, to server-side request forgery.
- You will gain an insight into measures that can help enhance the security of your own application during day-to-day development.
The workshop is aimed at software developers, architects and testers involved in the development of web applications.
Workshop details
1 day
On request
On-site at iteratec or online
Teams of up to 14 people
Process – How we proceed
-
A change of perspective: attack rather than defence
To better identify and understand security vulnerabilities in the development process, adopt an attacker’s perspective
-
Virtual training environment
With the OWASP Juice Shop, we provide you with a virtual training environment that can be accessed via the internet
-
Attack drills
As part of a series of hands-on exercises, you will attack this system and, in doing so, learn about the key attack vectors
-
Personalised training programmes
We will work with you to determine the exact content of the training. For example, we can make targeted use of the tools and software you specify
Coaches – The people who turn you into a champion
To cover all our services, we work with a team of three people who possess extensive expertise in software development, architecture and security. Meet our trainers:
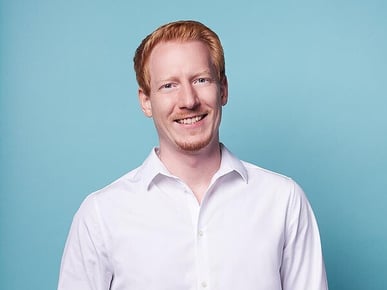
Martin Lang
As a Lead Software Engineer, Martin has been developing professional software for over 10 years and has worked across various industries and project environments. In his role as an IT Security Consultant, his focus is primarily on web application security and the interplay between security and software development.
Christian Mailer
As an IT Security Architect, Christian has been working on a wide variety of projects for over 20 years, focusing on the agile development of, most recently, cloud-native Java applications. From very early on, he has always kept a close eye on the various aspects of system and application security.
Michael Lörscher
Michael is an IT security architect. He has been developing innovative web applications for 13 years. Drawing on his many years of experience and his specialisation in application security, he helps leading clients to secure their systems.
We look forward to seeing you!
Secure training slots for your team – with no obligation and hassle-free. Do you have any questions about our training programme, availability or costs? Please get in touch.