THREAT MODELLING: IDENTIFYING RISKS INDEPENDENTLY
- Solutions
- Threat Modeling
What is threat modelling?
Every organisation’s IT applications and software development processes are regularly targeted by cyberattacks – this is inevitable. It is better to be prepared and to understand how attackers operate.
Threat modelling allows potential threats or risks to a software application or system to be identified by assessing their security requirements and the associated risks. The key question is: what could possibly go wrong?
Identifying threats before they arise
Threat modelling is used in software development to identify potential security issues in software design at an early stage. This involves analysing the components of an application or system and creating threat scenarios that describe possible attack vectors and vulnerabilities.
Threat modelling often reveals fundamental issues that are not necessarily related to IT systems – such as vulnerable processes, data flows or storage locations.
Threat modelling uncovers fundamental flaws
Threat modelling does not focus on traditional bugs – that is, shortcomings in code quality or typical programming errors – but rather analyses security design flaws. These are fundamental errors in software design, in the technical concept or in relation to the requirements. These flaws can only be identified with contextual knowledge, which is why their analysis cannot be automated. If they are not detected in good time, remedial measures are often time-consuming and costly.
Thanks to threat modelling, developers and IT security experts can gain a better understanding of the system or application and thus protect it more effectively. Furthermore, measures can be taken to improve security, such as implementing encryption technologies, introducing access controls or hardening network components.
Our workshop programme: Threat modelling with the whole team
To help your organisation make the most of threat modelling, we offer workshops tailored to your needs, focusing on the identification and assessment of security risks and countermeasures.
Following the workshop, participants will take a better understanding of vulnerabilities back with them to their day-to-day work. The methodology helps all those involved to make the topic of IT security tangible and to derive concrete measures that can be scheduled in the project backlog.
Workshop participants will learn the methodology and approach required to consciously put themselves in the shoes of an attacker. This will enable them to independently identify the key business and technical risks.
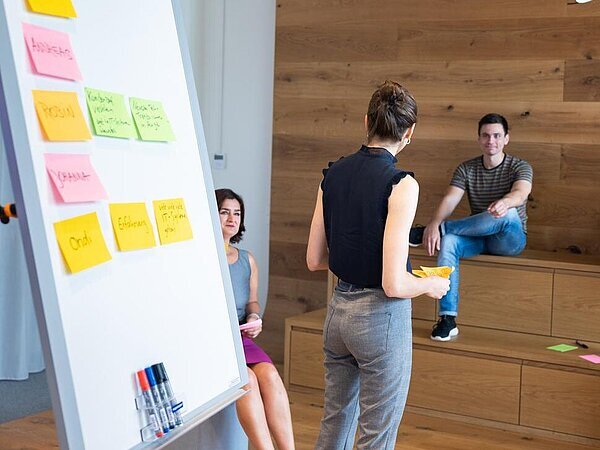
Key details of our workshop
- Interactive workshop format
- Focus on your specific core applications
- Duration: 1 day or 2 half-days
- 2 security experts with extensive experience in software engineering
- Max. 12 participants
- Includes preparatory and follow-up work
- Can be delivered online or in person
- In German or English
Developing security in an agile way
Methodologically, our agile workshops are based on the STRIDE framework. We take a holistic view of the system and identify specific threats in the form of so-called ‘evil user stories’, in order to derive and prioritise targeted countermeasures.
Benefits of Threat Modelling
A CHANGE OF PERSPECTIVE
By swapping roles with the attacker, a different perspective is gained, revealing vulnerabilities and enabling a fresh view of the security architecture.
IN-DEPTH ANALYSIS
Threat modelling identifies fundamental flaws in the architecture at an early stage, thereby enabling effective and sustainable improvements to IT security.
DO IT YOURSELF
Together, we’ll lay the foundations for your team to independently identify new security threats and implement countermeasures.
Your contact
Would you like to know how to systematically address key security issues and integrate IT security into your development processes from the outset? Please feel free to send me a message and I will get back to you.
Sven Strittmatter, Software Architect and Security Consultant
FAQ
Threat modelling is a structured method for the systematic identification and assessment of security risks, in which potential attack vectors, threat actors and the security requirements of a solution are analysed in order to identify security vulnerabilities at an early stage of the design process.
Threat modelling enables potential security risks to be identified as early as the planning and architecture phase, before they manifest themselves in the code, thereby reducing the need for costly rectifications later on and enhancing the quality and security of the entire solution.
Threat modelling should ideally be carried out early in the development process – for example, during architectural planning or before major changes – to ensure that risks can be addressed at the design stage.
iteratec runs agile threat modelling workshops based on the STRIDE framework, in which the system as a whole is examined and specific threats are described as ‘Evil User Stories’. Targeted countermeasures are then derived and prioritised on this basis, in order to integrate security into the development process at an early stage and in a structured manner.
iteratec offers an interactive threat modelling workshop tailored to specific applications. Participants learn to identify security risks and countermeasures, put themselves in the shoes of attackers, and derive specific actions for the project backlog – led by experienced security experts, either online or on-site.