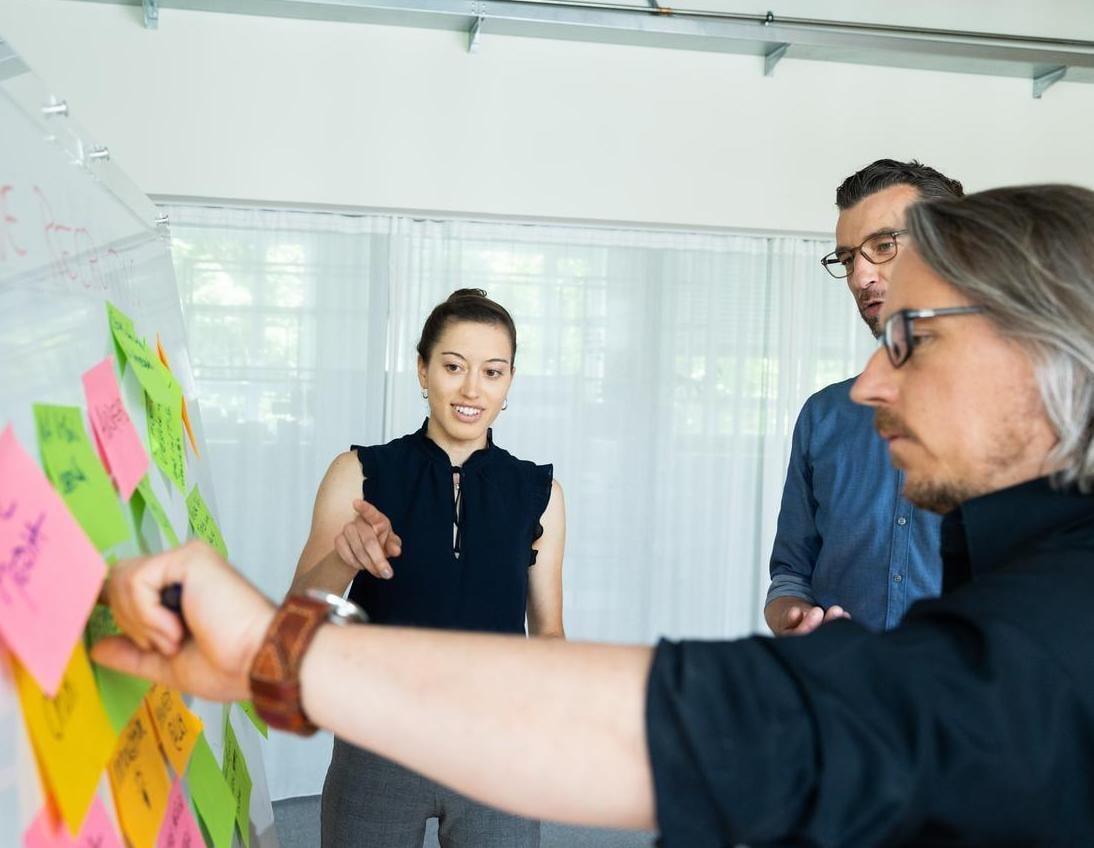
THREAT MODELLING WITH THE WHOLE TEAM
- Services
- AI-centred Security
- Trainings & Workshops
- Threat Modelling Workshop
Threat Modelling Workshop
To help your organisation make the most of threat modelling, we offer workshops tailored to your needs, focusing on the identification and assessment of security risks and countermeasures.
Following the workshop, participants will take a better understanding of vulnerabilities back with them into their day-to-day work. The methodology helps all those involved to make the topic of IT security tangible and to derive concrete measures that can be scheduled in the project backlog.
Workshop participants learn the methodology and approach required to consciously put themselves in the shoes of an attacker. This enables them to independently identify the key business and technical risks .
Key details of our workshop
- Interactive workshop format
- Focus on your specific core applications
- Duration: 1 day or 2 half-days
- 2 security experts with extensive experience in software engineering
- Max. 12 participants
- Includes preparatory and follow-up work
- Can be delivered online or in person
- In German or English
Workshop details
1 day or 2 half-days
4,050 euros
On-site at iteratec or online
Teams of up to 12 people
Process – How we proceed
-
Kick-off & Initial Assessment
Joint assessment of the current state of your applications, including an architecture review, an OWASP-based vulnerability analysis and, where appropriate, a quick check (light penetration test)
-
Interactive workshop (1 day or 2 half-days)
Threat analysis with your team using the STRIDE methodology – component-, role- and scenario-based
-
Identification and Assessment of Threats
Description of specific risks as ‘Evil User Stories’, assessment of criticality (probability of occurrence and extent of damage), derivation of countermeasures
-
Identification of specific measures
The identified risks are translated into specific security measures that can be incorporated directly into the project backlog
-
Team training and development
Fostering security awareness and methodological skills to enable individuals to independently identify and address future threats
The workshop is aimed at interdisciplinary teams responsible for the development, security and architecture of IT applications.
The following will benefit in particular:
- Software developers who want to consider and implement security from the outset (‘Shift Left’, DevSecOps).
- Security champions and those who would like to take on this role within their team.
- IT architects who wish to embed security considerations into the system architecture.
- Project managers and product owners who wish to understand and prioritise risks and integrate them into the backlog as actions.
- IT security officers and security managers who wish to strengthen governance, processes and awareness within the organisation.
The threat analysis is designed as an interactive session for the entire project team – practical, role-based and accessible to all participants. No prior knowledge is required.
Coaches – The people who turn you into a champion
To cover all our services, we work with a two-person team that brings extensive experience in software development, IT architecture and application security. Our trainers combine sound technical expertise with many years’ experience of running workshops – they take a practical approach, are skilled in their methodology and have a keen understanding of the challenges faced by modern development teams.
Meet one of our trainers:
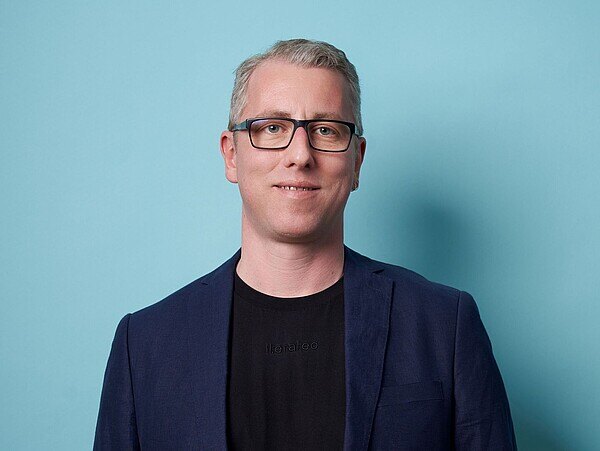
Sven Strittmatter
As a software architect and security consultant at iteratec, Sven has been working on various projects since 2015, focusing on the holistic implementation of company-wide security measures. Over the course of his more than 15 years’ professional experience, he has learnt about security ‘the hard way’.